

See what attackers see before they do.
RidgeBot is an AI-powered security validation platform from Ridge Security that helps organisations identify, validate and prioritise exploitable cybersecurity weaknesses before they become incidents.
Whether a customer needs a targeted once-off penetration test or continuous, always-on security validation, Smart Hands Africa helps partners deliver a practical, credible cybersecurity service under their own brand.
Most organisations have more vulnerability information than they can act on. Traditional security testing can be expensive, time-consuming and performed only once or twice a year—leaving long periods where new weaknesses can emerge unnoticed.
RidgeBot goes beyond identifying potential vulnerabilities. It safely validates whether a weakness can actually be exploited, shows the potential attack path and helps teams focus remediation on the risks that matter most.
A once-off penetration test is ideal when a customer needs an independent assessment of a specific environment, application, external attack surface or compliance requirement.
RidgeBot automates much of the penetration-testing process, enabling a focused, repeatable assessment that safely simulates real attacker behaviour. The result is a clear picture of exploitable weaknesses, attack paths and recommended remediation actions.
Compliance, audit or customer assurance requirements
A new website, application, API or infrastructure rollout
Pre-launch or pre-production testing
A specific security concern or suspected weakness
Customers that need a starting point for a broader cybersecurity programme
Cyber risk does not wait for the next annual test. New vulnerabilities, configuration changes, applications and attack techniques can create exposure throughout the year.
RidgeBot provides continuous security validation by automatically discovering, testing and validating weaknesses on a scheduled or on-demand basis. It helps customers move from a point-in-time assessment to an ongoing, evidence-based view of their cybersecurity posture.
Organisations with changing IT environments
Businesses with multiple sites, applications or cloud workloads
Customers handling sensitive data
Organisations that need ongoing compliance and assurance evidence
MSP customers that need a managed cybersecurity service
Development teams working within DevSecOps or secure software-development practices
RidgeBot identifies the assets that form part of the customer’s attack surface, including IP addresses, domains, hosts, operating systems, applications, websites, databases and cloud-connected environments.
It uses AI-driven decision-making, security knowledge and attack techniques to assess the environment for weaknesses.
Rather than simply flagging a theoretical vulnerability, RidgeBot safely attempts to validate whether it can be exploited in the customer’s real environment.
Validated risks are placed in context according to exploitability, attack path and potential impact—helping teams focus on what deserves attention first.
Clear remediation guidance helps technical teams address the issue. RidgeBot can then retest to help confirm whether the weakness has been resolved.
OMNIA gives partners a compelling way to combine connectivity, cybersecurity and managed services into one clear monthly offering.
Instead of selling a collection of products, you can help customers solve a real business problem: staying connected, protected and visible as their business grows.
Test static and dynamic websites, including authenticated applications, for common risks such as authentication weaknesses, session risks and OWASP Top 10 vulnerabilities.
Test APIs for vulnerabilities in endpoints, authentication, data exchange and configuration, including risks such as broken authentication and injection attacks.
Simulate the potential impact of an attacker who already has a level of access, helping customers understand how far an attack could spread from a compromised account or device.
Assess how an attacker could move from one compromised system to another, escalate privileges and reach deeper parts of the environment.
Test the effectiveness of security controls by simulating realistic adversary tactics and techniques, aligned to the MITRE ATT&CK framework.
Support testing across cloud and hybrid environments, helping customers assess the security of assets, applications and services beyond the traditional network perimeter.
Offer continuous AI-based testing as a subscription-led managed security service.
Use an assessment to reveal risk, establish trust and open the door to recurring validation, remediation and broader cybersecurity services.
Deliver a professional cybersecurity service that strengthens your own customer proposition.
SHA can support deployment, reporting, service delivery and technical escalation where required.
RidgeBot is a natural value-add for partners already managing IT infrastructure, cloud, networks, applications or cybersecurity.
Validated findings can lead to remediation projects, managed security, compliance reporting, API testing, cloud security and ongoing advisory work.
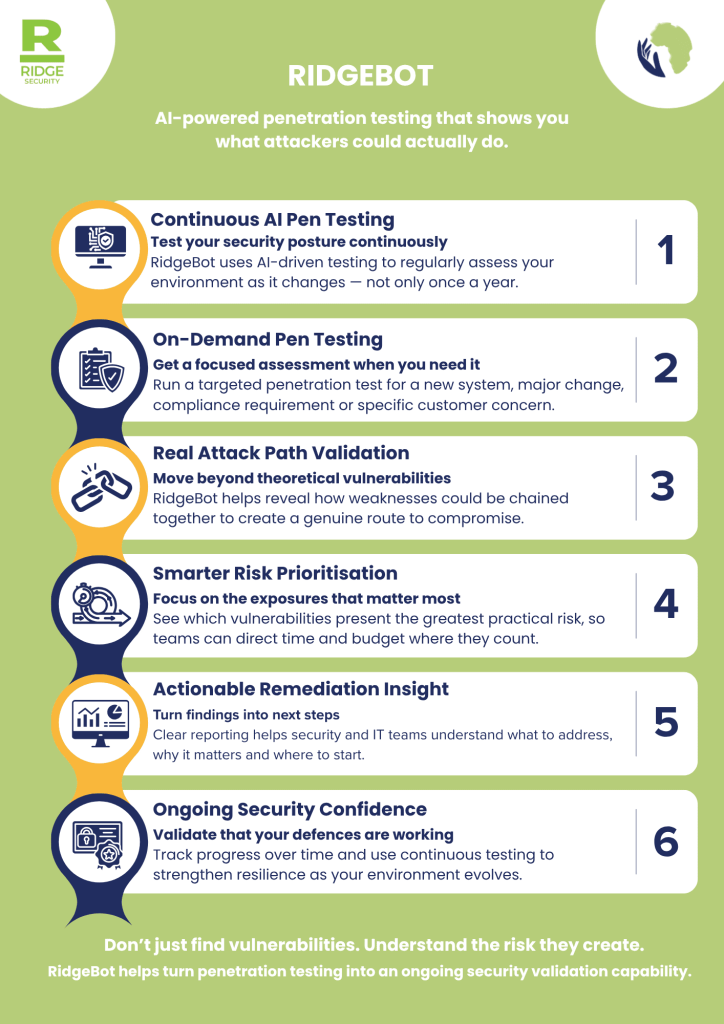
RidgeBot is an AI-powered security validation platform from Ridge Security. It automates penetration testing, discovers attack surfaces, safely validates exploitable vulnerabilities and provides prioritised remediation guidance.
RidgeBot does more than scan. It can safely test and validate whether identified vulnerabilities can be exploited in the real environment, helping customers distinguish theoretical findings from meaningful security risks.
A once-off penetration test provides a detailed assessment at a specific point in time. Continuous testing uses scheduled or ongoing automated validation to help organisations identify new exposures as their environment, applications and threats evolve.
RidgeBot automates and accelerates many penetration-testing activities, making more frequent security validation practical. Some customers may still require specialist manual testing for highly specific, complex or regulated scenarios. The right model depends on the customer’s environment and requirements.
RidgeBot is designed to use controlled, ethical attack techniques and includes safety measures intended to minimise disruption. Every engagement should be correctly scoped, authorised and configured before testing begins.
RidgeBot can support testing across networks, infrastructure, web applications, authenticated applications, APIs, cloud environments and other connected assets, subject to the agreed scope and deployment model.
RidgeBot can provide evidence-based reporting and support relevant security-assessment requirements. It also supports reporting aligned to areas such as OWASP Top 10 for web application testing. Partners should confirm the precise compliance requirement for each customer.
Yes. RidgeBot can support a white-label managed-service model, including co-branded reporting, allowing partners to deliver a stronger cybersecurity service while SHA supports the technical capability behind it.
Start by identifying an existing customer with sensitive data, compliance needs, exposed applications, limited in-house security skills or a need for clearer risk visibility. A once-off assessment is often an effective entry point, followed by a continuous validation service where appropriate.
SMART HANDS AFRICA offers best-in-class product solutions provided by innovative brands


Start with a targeted assessment or build a recurring continuous-security-validation service. Smart Hands Africa gives you the RidgeBot capability, delivery support and partner model to make either opportunity work.