Firewalls, vulnerability scans and annual penetration tests all play an important role. But applications change, configurations shift and new vulnerabilities emerge throughout the year.
Passing an audit confirms your position at a specific moment. It does not mean you remain secure.
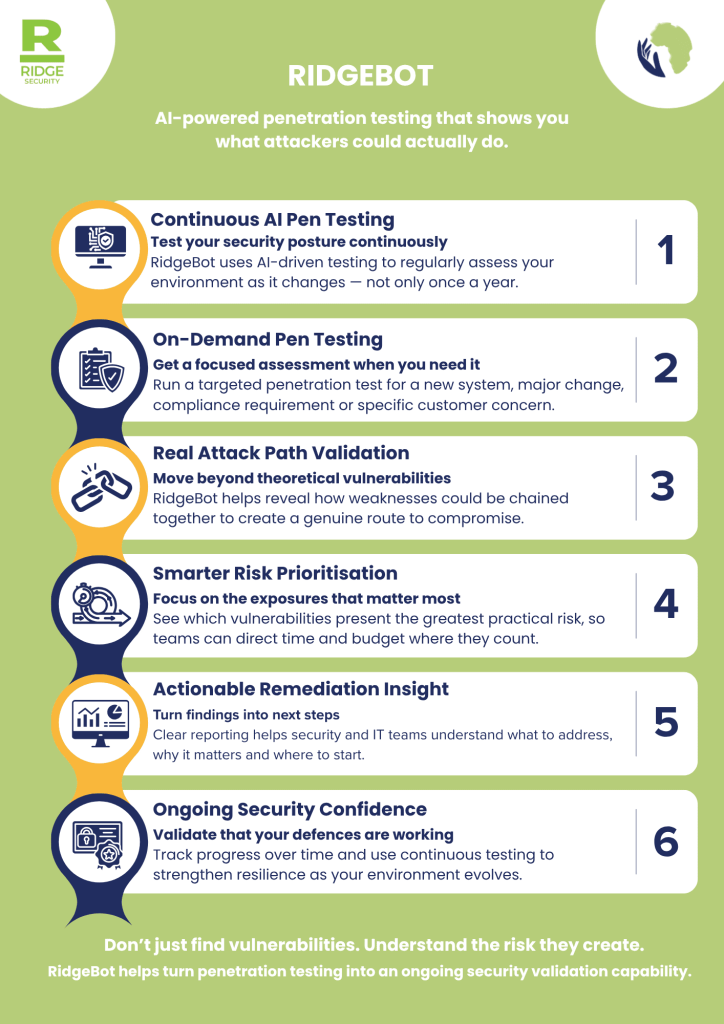
RidgeBot adds continuous, automated penetration testing to your cybersecurity strategy—helping you move from assuming your controls work to regularly validating them.
Identifies potential weaknesses that may require investigation.
Uses specialist expertise to test exploitability, but usually provides a point-in-time view.
Automates repeatable penetration testing to validate exploitable risks as your environment changes.
Maps assets across your agreed attack surface.
Uses AI-driven decision-making and recognised attack techniques to assess potential weaknesses.
Safely tests whether identified vulnerabilities can be exploited in your environment.
Places validated risks in the context of their attack path, exploitability and potential impact.
Provides practical remediation guidance and can retest to help confirm that fixes have worked.
RidgeBot identifies the assets that form part of the customer’s attack surface, including IP addresses, domains, hosts, operating systems, applications, websites, databases and cloud-connected environments.
It uses AI-driven decision-making, security knowledge and attack techniques to assess the environment for weaknesses.
Rather than simply flagging a theoretical vulnerability, RidgeBot safely attempts to validate whether it can be exploited in the customer’s real environment.
An independent assessment of a defined environment, application, API or external attack surface.
Ideal for:
Compliance and assurance
New or pre-launch systems
Specific security concerns
Establishing a security baseline
Automated testing that provides ongoing, evidence-based insight into your changing security posture.
Ideal for:
Growing or changing IT environments
Multiple sites, applications or cloud workloads
Sensitive-data protection
Ongoing compliance and assurance
DevSecOps and managed security services
No. Vulnerability scanners identify possible weaknesses. RidgeBot goes further by safely testing whether weaknesses can be exploited, helping teams separate theoretical alerts from meaningful risks.
RidgeBot automates and accelerates many penetration-testing activities, making more frequent validation practical. Specialist manual testing may still be appropriate for highly specific, complex or regulated requirements.
RidgeBot is designed to use controlled, ethical testing techniques with measures intended to minimise disruption. Every engagement must be correctly scoped, authorised and configured before testing begins.
RidgeBot provides evidence-based reporting that can support relevant security-assessment and assurance requirements. The precise requirements should be confirmed for each organisation and regulatory framework.
No. RidgeBot is scalable and can support growing businesses as well as complex enterprise environments.

Move beyond point-in-time assumptions. Discover which weaknesses are genuinely exploitable, focus your resources on the risks that matter and continuously validate that your security controls are working.
Complete the form and a Smart Hands Africa specialist will contact you to discuss the RidgeBot option that best fits your organisation.
SMART HANDS AFRICA offers best-in-class product solutions provided by innovative brands